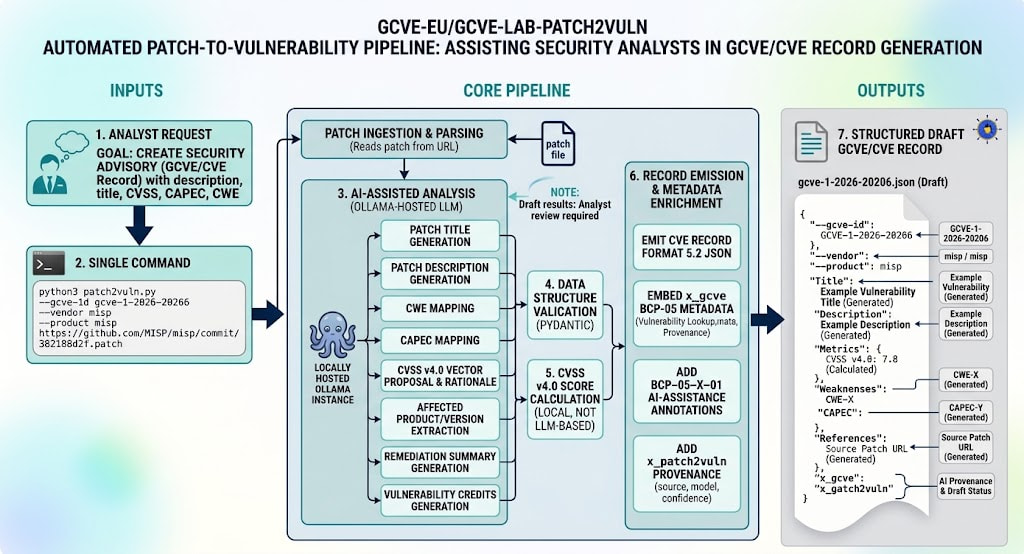
2026-09-18 (Friday) Journal
Day summary: Today’s RSS activity: 3 item(s) from discourse.ossbase.org, infosec.exchange including “GCVE Lab - patch2vuln is a command-line tool that turns a git-format patch into a structured draft vulnerability advisory using a locally hosted Ollama model”; “Tired of drafting vulnerability advisories from Git patches?We developed patch2vuln to facilitate the creation of security advisories directly from Git patches.With a single command, patch2vuln can assist an analyst throughout the advisory creation process: analyzing the patch, drafting the vulnerability title and description, identifying CWE and CAPEC mappings, proposing a CVSS v4.0 vector, extracting affected versions, remediation information and credits, and generating a structured CVE/GCVE record.The analysis can run entirely locally using an LLM via Ollama, while deterministic processing is used for elements such as CVSS scoring and structured output validation.The goal is not to replace the security analyst, but to remove much of the repetitive work and provide a solid structured draft for human review and publication.patch2vuln v1.0 is now available as open-source software under the @gcve Lab initiative.https://gcve.eu/2026/09/18/introducing-patch2vuln-v1.0-streamlining-vulnerability-advisory-creation-from-git-patches/Thanks to David Cruciani for the tests and Jeroen Pinoy for the initial feedback.#VulnerabilityManagement #CVD #CVE #GCVE #OpenSource #CyberSecurity #AI”.
Hourly activity:
hour  00 01 02 03 04 05 06 07 08 09 10 11 12 13 14 15 16 17 18 19 20 21 22 23
pulse  .  .  .  .  .  .  @  .  .  .  .  .  .  .  .  @  @  .  .  .  .  .  .  .
count 00 00 00 00 00 00 01 00 00 00 00 00 00 00 00 01 01 00 00 00 00 00 00 00
GCVE Lab - patch2vuln is a command-line tool that turns a git-format patch into a structured draft vulnerability advisory using a locally hosted Ollama model
- Source:
discourse.ossbase.org - Time:
16:04:34 - Summary: Published on GCVE website
gcve.eu – 18 Sep 26 Introducing patch2vuln v1.0: Streamlining Vulnerability Advisory Creation… GCVE Workshop Before The Vulnopticon Conference
Tired of drafting vulnerability advisories from Git patches?We developed patch2vuln to facilitate the creation of security advisories directly from Git patches.With a single command, patch2vuln can assist an analyst throughout the advisory creation process: analyzing the patch, drafting the vulnerability title and description, identifying CWE and CAPEC mappings, proposing a CVSS v4.0 vector, extracting affected versions, remediation information and credits, and generating a structured CVE/GCVE record.The analysis can run entirely locally using an LLM via Ollama, while deterministic processing is used for elements such as CVSS scoring and structured output validation.The goal is not to replace the security analyst, but to remove much of the repetitive work and provide a solid structured draft for human review and publication.patch2vuln v1.0 is now available as open-source software under the @gcve Lab initiative.https://gcve.eu/2026/09/18/introducing-patch2vuln-v1.0-streamlining-vulnerability-advisory-creation-from-git-patches/Thanks to David Cruciani for the tests and Jeroen Pinoy for the initial feedback.#VulnerabilityManagement #CVD #CVE #GCVE #OpenSource #CyberSecurity #AI
- Source:
infosec.exchange - Time:
15:55:27 - Summary: GCVE records generated from the AI-assisted tool with the BCP extension seen in vulnerability-lookup interface.
GCVE Lab - patch2vuln is a command-line tool that turns a git-format patch into a structured draft vulnerability advisory using a locally hosted Ollama model
- Source:
discourse.ossbase.org - Time:
06:38:04 - Summary: The latest version of
patch2vulngithub.com GitHub - gcve-eu/gcve-lab-patch2vuln: patch2vuln is a command-line tool that turns a… patch2vuln is a command-line tool that turns a git-format patch into a structured draft vulnerability advisory using a locally hosted Ollama model. and a global overview:
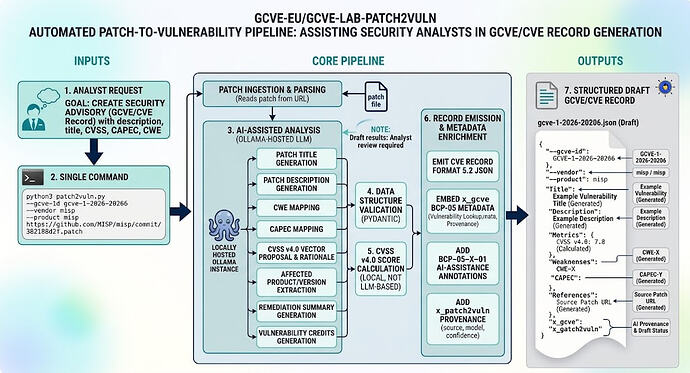 The project was tested in different use-cases and will most probably go out of…